Building an internal Security Operations Centre (SOC) gives an organisation direct control over its security operations. But what does it actually take to keep one running around the clock?
At first, the calculation might seem relatively straightforward. Recruit security analysts, invest in the right technology and organise a shift rota. In reality, maintaining genuine 24/7 security monitoring and response involves a much larger operational commitment.
Staffing is only one part of the picture. Recruitment, training, technology, management and the capacity to maintain coverage throughout the year all contribute to the overall investment.
For organisations considering an internal SOC, understanding these less visible costs is essential when comparing the options available.
How many analysts does a 24/7 SOC need?
To keep just one analyst seat staffed around the clock, you need a team of at least six people.
A 24/7 security operation needs someone available to monitor, investigate and respond to potential threats at any time. That means covering 168 hours every week, including nights, weekends and bank holidays.
On a standard 37.5-hour working week, those hours alone require approximately 4.5 full-time equivalents (FTEs). Once UK statutory holiday entitlement (5.6 weeks a year), sickness, training and a workable shift rota are factored in, the absolute minimum becomes six.
Even six is lean. It leaves very little room for a resignation, long-term sickness or a sudden rise in incidents. Six salaries, plus employer costs, every year, just to keep one position covered, before any technology, training or recruitment. Our in-house SOC cost calculator can help you estimate what that looks like for your organisation.
A larger SOC may need several analysts on shift at the same time, alongside senior escalation support, security engineering and incident response expertise. Having enough people to fill a rota on paper is very different from having the capacity to run a reliable operation all year round.
The hidden costs of 24/7 SOC staffing
Staffing is likely to be the largest ongoing expense, but the cost extends beyond the number of people employed.
Recruitment and analyst turnover
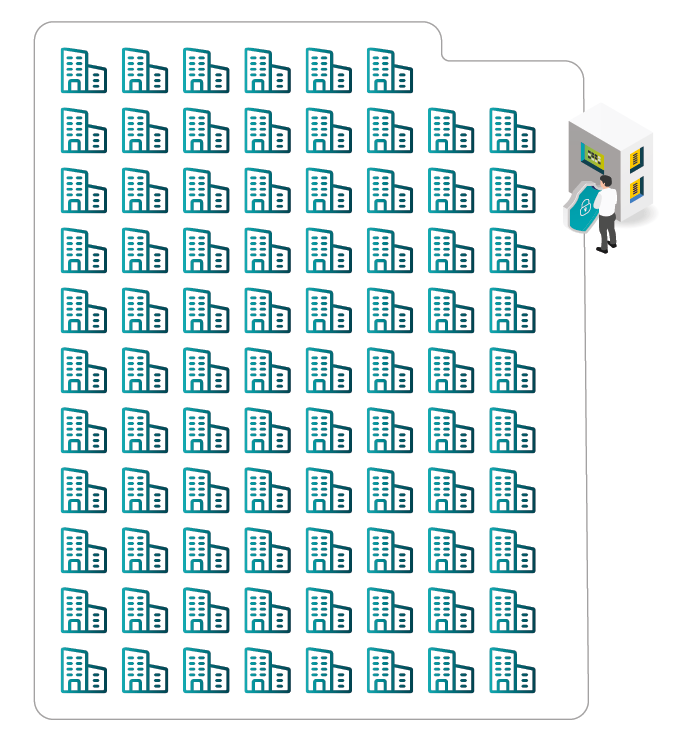
Finding experienced security professionals can be challenging. Our analysis of ONS data found there is just one cyber security professional for every 68 UK businesses. Recruitment involves more than advertising a vacancy and interviewing candidates. There may be agency fees, onboarding, background checks and the time required to bring someone up to speed with your organisation’s environment and processes.
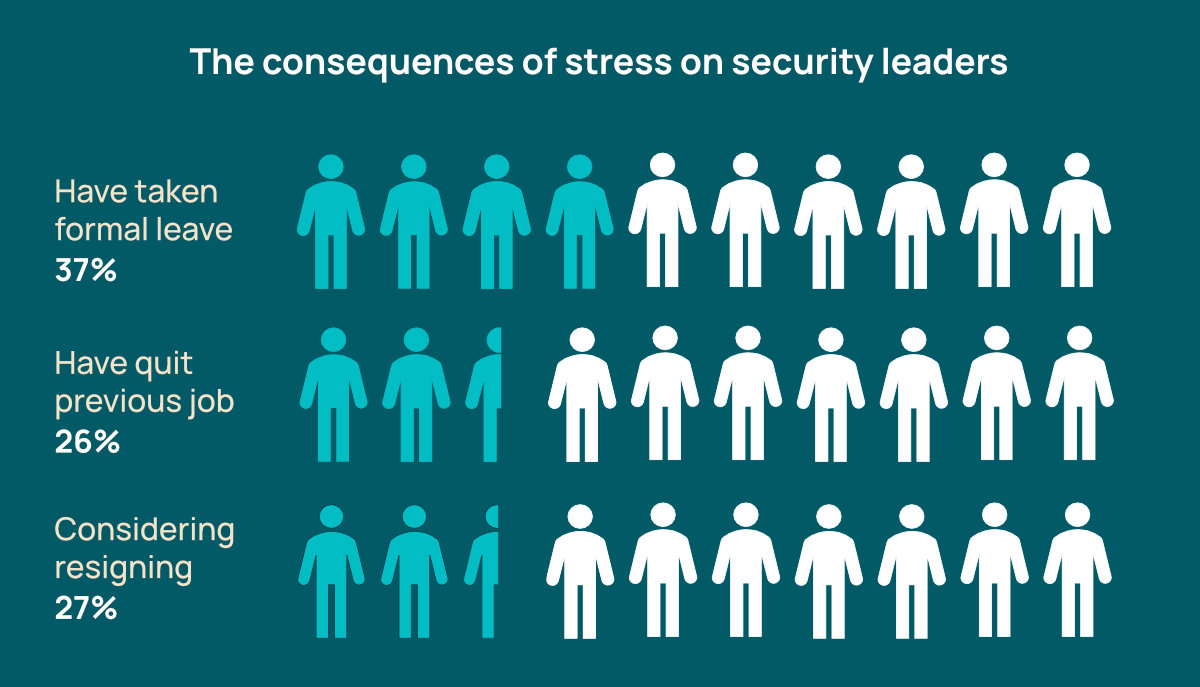
Then there is the possibility of turnover. When an analyst leaves, their responsibilities still need to be covered. Other team members may have to take on additional shifts while a replacement is recruited and trained. This can put pressure on the remaining team and create further recruitment and onboarding costs.
For an organisation operating around the clock, even one departure can have a disproportionate impact on a relatively small team.
Training and professional development
Cyber security is constantly evolving. Analysts need to keep up with new attack techniques, emerging threats, changing technologies and the tools they use to investigate suspicious activity.
Ongoing training, professional certifications and development are therefore essential, not optional extras.
Training also has an operational cost. Time spent developing skills is time away from monitoring and investigation, so the organisation needs sufficient staffing capacity to maintain coverage while people undertake it.
Shift allowances and operational resilience
Night shifts, weekends and bank holidays can introduce additional employment costs, depending on the organisation’s arrangements.
There is also the question of resilience. What happens when an analyst is unavailable due to illness, annual leave or an unexpected absence?
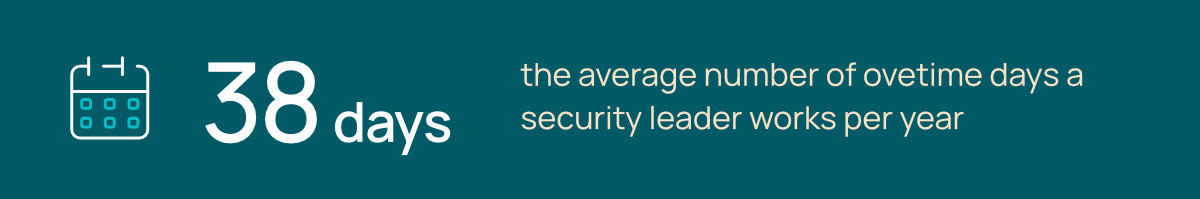
Relying on a small number of individuals to cover gaps can increase pressure, contribute to fatigue and make long-term retention more difficult.
A sustainable operation needs enough capacity to manage these situations without compromising security monitoring and response.
Security technology is another significant investment
People alone do not make a SOC. Analysts need the right technology to collect security data, identify suspicious activity and support investigations.
Depending on the organisation’s environment and requirements, this may include several of the following.
The more complex the environment, the more consideration needs to be given to integration, data retention, licensing and ongoing optimisation. Technology also needs to be configured, maintained and regularly reviewed to remain effective, which may require additional specialist expertise.
AI is becoming part of the toolkit too. It can help analysts triage alerts and cut through noise, but it still needs skilled people to set it up, check its output and make the final call. It makes a good team faster and more robust. It does not replace the team.
What does the full investment look like?
When all these elements are considered together, the financial commitment becomes clearer. An organisation needs to account for several areas beyond the initial recruitment and technology costs.
The exact investment will vary depending on the organisation’s size, environment and security requirements. However, the combined cost of maintaining the people, technology and processes needed for continuous operations can be substantial.
Is building an internal SOC the right investment?
An internal SOC can be a sensible investment for organisations with the resources, scale and operational requirements to support one.
It offers direct control over people, technology, processes and priorities. It can also allow analysts to develop detailed knowledge of the organisation's environment and work closely with internal IT and security teams.
However, the decision should be based on the full cost of delivering that capability, not simply the appeal of having an internal team.
A co-managed arrangement may provide a more practical balance for some organisations, retaining internal security expertise while using an external provider to extend coverage. For others, fully outsourced MDR may be a better fit, providing access to continuous monitoring, investigation and response without the responsibility of building and maintaining the entire operation.
The important thing is to compare like with like. Consider the people, technology, coverage and responsibilities included in each option, rather than comparing an MDR service against the cost of employing a single analyst.
Our guide to co-managed SOC vs outsourced MDR explores these different approaches in more detail.
Making the cost comparison
Building a 24/7 internal security team is a substantial operational commitment. The investment extends across staffing, recruitment, training, technology and the capacity needed to maintain reliable coverage.
Socura’s Core MDR service offers an alternative, providing 24/7 security monitoring and access to specialist UK-based analysts, so organisations can maintain continuous security operations without having to build the entire capability themselves. Our analysts utilise AI to help triage alerts and speed up investigations, but decisions always stay with experienced people.
Ultimately, the decision is about understanding what genuine 24/7 security operations require, assessing the full cost of delivering them internally and deciding where your organisation’s resources are best invested.
The objective is to have the right security capability in place, sustainably and when it matters.